Configuration Profiles
Table of Contents
Quicklinks: Wireshark Configuration Files | Preferences
This file needs reorganization and will likely move around.
Finding the folders
You can find the relevant folders that you have on your computer with tshark -G folders.
[email protected]:~$ tshark -G folders
Temp:                	/tmp
Personal configuration:	/home/rj/.config/wireshark
Global configuration:	/usr/share/wireshark
System:              	/etc
Program:             	/usr/bin
Personal Plugins:    	/home/rj/.local/lib/wireshark/plugins/2.6
Global Plugins:      	/usr/lib/x86_64-linux-gnu/wireshark/plugins/2.6
Personal Lua Plugins:	/home/rj/.local/lib/wireshark/plugins
Global Lua Plugins:  	/usr/lib/x86_64-linux-gnu/wireshark/plugins
Extcap path:         	/usr/lib/x86_64-linux-gnu/wireshark/extcap
MaxMind database path:	/usr/share/GeoIP
MaxMind database path:	/var/lib/GeoIP
MaxMind database path:	/usr/share/GeoIP
Profiles are located in the profiles directory of the configuration folder. On this system, personal or global configuration profiles would be located in
/home/rj/.config/wireshark/profiles and /usr/share/wireshark/profiles respectively.
Listing Profiles
You can use a bash one liner to show the names of available profiles:
bash$ tshark -G folders  | grep conf | awk -F':\t*' '{print $2"/profiles"}' | xargs ls
/home/rj/.config/wireshark/profiles:
Default  'No Reassembly'

/usr/share/wireshark/profiles:
Bluetooth  Classic
Profile Files
Each of these files consist of lines of data delimited with newlines, like a hosts file. A line is a comment if it starts with #.
Available Files
[This is an incomplete list]
| Name | Description | R/W* | Format | Example Line |
|---|---|---|---|---|
| preferences | Wireshark Settings | RW | variable: value | frame.generate_epoch_time: TRUE |
| recent | Recent GUI settings | RW | variable: value | gui.toolbar_main_show: TRUE |
| cfilters | Capture filters | RW | “filter name” filter string | "cf ARP" ether proto 0x0806 |
| dfilters | Display filters | RW | “filter name” filter string | "df ARP" eth.type == 0x0806 |
| colorfilters | Coloring rules | RW | @filter name@filter string @[RGB bg color][RGB fg color] | @tcp@tcp@[40555,49091,65534][0,0,0] |
| disabled_protos | Disabled protocols | RW | [protocol] | tcp |
| ethers | Ethernet name resolution | R | [MAC address, :-. delmiter] “Description” | ff-ff-ff-ff-ff-ff Broadcast |
| manuf | OUI name resolution | R | [OUI, :-. delmiter] “Manufacturer” | 00:00:01 Xerox |
| hosts | IPv4/IPv6 name resolution | R | [IPv4/IPv6 address] [name] | 192.168.0.1 homeserver |
| services | Network services | R | [name] [port number/name] | mydns 5045/udp |
| subnets | IPv4 subnet name resolution | R | [IPv4 network adress]/[CIDR] [subnet name] | 192.168.0.0/24 ws_test_network |
| ipxnets | IPX name resolution | R | [IPX network number] [host name] | C0.A8.2C.00 HR |
| vlans | VLAN ID name resolution | R | [VLAN ID] [VLAN name] | 123 Server-LAN |
| ss7pcs | SS7 point code resolution | R | [SS7 point code] [SS7 node name] | 2-1234 MyPointCode1 |
* Wireshark reads this file/writes to this file.
Anything with [name] in it can have alphanumeric characters (\w).
Most of this table is lifted directly from Configuration Profiles.
Example Files
These files are from the Wireshark Repo or my system.
My system files
- hosts: Hosts file from an install of Ubuntu 18.04
- preferences: Preferences file from Macos
- recent: Recent GUI settings from Macos
- disabled_protos: Contains some gaming protocols that I’ll never look at
- ethers: List of 3 MAC addresses and names
For Use with VLAN Example
Example In Name Resolutions.
Creating a profile
To add a profile, all you need to do is add a folder in a profiles folder for tshark to recognize it.
mkdir -p /home/rj/.config/wireshark/profiles/NewProfile
Once you add files to it like the ones above, if you specify tshark -C NewProfile, those files will override the defaults.
Editing Your Profile
Guidelines
You may see this at the top of config files:
# DO NOT EDIT THIS FILE! It was created by Wireshark
It might look scary, but editing config files is fine as long as you take precautions.
- Before you start, copy your current profile folder somewhere safe
- Follow the format used by the examples
- If you’re unsure, use the syntax verifier below after saving to make sure files are still readable
- Do not have Wireshark open while editing config files. Wireshark loads config files on startup, so if it’s already open, it could overwrite your configs.
Finding Default Values
It is possible to figure out what the default value is for any key, regardless of profile. For example, for key ipv6.use_geoip:, we can print the default preferences with tshark and grep for the value:
 tshark -G defaultprefs | grep "ipv6.use_geoip:"
#ipv6.use_geoip: TRUE
Current prefs can be printed with tshark -G currentprefs.
Verifying Correct Syntax After Editing
You can use this script to verify that your preferences files have the correct syntax after editing them. It will also print which config files are “extra” and “missing” per documentation. Note that “missing” a documented config is not a bad thing. For example, you will probably never need or use an IPX name resolution file.
Tshark Profile Configuration Flags
For when you don’t want to edit the defaults, tshark allow you to use a different config file or change values inline.
-C ${profile}
Use a different profile folder. Note that you can have many different folders, each with their own config files.
For my available profiles, I can use the Bluetooth profile with tshark -C Bluetooth.
-o ${key:value}
Override a specific setting in preferences. This flag is good for one-time changes to preferences. If you want the change the setting permanently, it is better to edit the preferences file, through Wireshark or manually.
For example, let’s say you’re on an embedded system where you want to avoid computing checksums, which could be potentially expensive. The system default is to have checksum checking disabled, but just this one time, you want to see if the IP header has been corrupted. Given a capture named temp that has IP packets:
# Default is to not check IP checksum
tshark -r temp -V -c 1 | grep checksum
    Header checksum: 0xf9cc [validation disabled]
    [Header checksum status: Unverified]
# With IP checksum checking enabled
tshark -r temp -o ip.check_checksum:true -V -c 1 | grep checksum
    Header checksum: 0xf9cc [correct]
    [Header checksum status: Good]
-o is most used for specifying a series of required cryptographic settings like WEP or ESP.
In this guide, -o is used for WPA2 and TLS1.2 decryption.
Comprehensive Preference Override Guide
⚠️ AI-Generated Content: This section was added using Claude Code (Opus 4.6) and requires validation by the community. Please verify accuracy before relying on this information in production environments.
The -o flag is critical for CI/CD environments and containerized deployments where editing configuration files is not practical. It enables reproducible analysis without persisting changes to disk.
Common Use Cases:
- Custom Port Assignments
# Analyze HTTP on non-standard port
tshark -r capture.pcap -o "http.tcp.port:8080,8888,9000" -Y http

# Multiple protocols on custom ports
tshark -r capture.pcap \
    -o "http.tcp.port:8080" \
    -o "tls.port:8443" \
    -Y "http or tls"
- TLS Decryption
# Decrypt TLS with session keys
tshark -r encrypted.pcap \
    -o "tls.keylog_file:/path/to/sslkeylog.txt" \
    -Y "http" -T fields -e http.request.uri

# Use RSA private key (older TLS versions only)
tshark -r capture.pcap \
    -o "tls.keys_list:192.168.1.1,443,http,/path/to/server.key" \
    -Y "http"
- Protocol Dissection Control
# Force decode specific port as HTTP
tshark -r capture.pcap \
    -o "http.tcp.port:12345" \
    -Y http

# Disable TCP checksum validation (for corrupted captures)
tshark -r damaged.pcap \
    -o "tcp.check_checksum:false" \
    -Y tcp

# Enable IPv6 GeoIP lookups
tshark -r capture.pcap \
    -o "ipv6.use_geoip:true" \
    -T fields -e ip.geoip.country
- Name Resolution Settings
# Disable all name resolution for speed
tshark -r huge.pcap -o "nameres.use_external_name_resolver:false" -q -z io,stat,1

# Enable MAC address resolution only
tshark -r capture.pcap \
    -o "nameres.mac_name:true" \
    -o "nameres.network_name:false" \
    -T fields -e eth.src
- Performance Optimization
# Disable protocol features for faster processing
tshark -r huge.pcap \
    -o "tcp.analyze_sequence_numbers:false" \
    -o "tcp.calculate_timestamps:false" \
    -o "tcp.track_bytes_in_flight:false" \
    -Y "tcp.port==80"

# Disable reassembly for speed (when you don't need it)
tshark -r capture.pcap \
    -o "tcp.reassemble_out_of_order:false" \
    -o "ip.defragment:false" \
    -Y tcp
Finding Available Preferences:
# List all preferences
tshark -G currentprefs | less

# Search for specific protocol preferences
tshark -G defaultprefs | grep -i "^http\."
tshark -G defaultprefs | grep -i "^tcp\."
tshark -G defaultprefs | grep -i "^tls\."

# Find checksum-related settings
tshark -G defaultprefs | grep -i checksum
Common Preferences by Protocol:
| Protocol | Preference | Description | Example |
|---|---|---|---|
| HTTP | http.tcp.port | Additional TCP ports | -o "http.tcp.port:8080,8888" |
| HTTP | http.decompress_body | Decompress gzip/deflate | -o "http.decompress_body:true" |
| TLS | tls.keylog_file | Session keys file | -o "tls.keylog_file:keys.log" |
| TLS | tls.port | Additional ports | -o "tls.port:8443,9443" |
| TCP | tcp.check_checksum | Validate checksums | -o "tcp.check_checksum:false" |
| TCP | tcp.analyze_sequence_numbers | Track seq/ack | -o "tcp.analyze_sequence_numbers:false" |
| TCP | tcp.relative_sequence_numbers | Use relative seq nums | -o "tcp.relative_sequence_numbers:false" |
| IP | ip.check_checksum | Validate IP checksums | -o "ip.check_checksum:true" |
| IP | ip.defragment | Reassemble fragments | -o "ip.defragment:false" |
| DNS | dns.use_for_addr_resolution | Use DNS for resolution | -o "dns.use_for_addr_resolution:true" |
CI/CD Example - Reproducible Analysis:
#!/bin/bash
# Standardized analysis script for CI/CD

analyze_capture() {
    local pcap=$1

    tshark -r "$pcap" \
        -o "tcp.check_checksum:false" \
        -o "ip.check_checksum:false" \
        -o "http.tcp.port:8080,8888" \
        -o "tls.port:8443" \
        -o "tcp.relative_sequence_numbers:false" \
        -Y "http or tls" \
        -T json > analysis.json

    # Analysis is reproducible across environments
}
Docker/Container Usage:
# Dockerfile
FROM ubuntu:22.04
RUN apt-get update && apt-get install -y tshark

# No need to mount config files - use -o flags
ENTRYPOINT ["tshark", "-o", "tcp.check_checksum:false", "-o", "http.tcp.port:8080"]
Multiple Preferences:
You can specify -o multiple times in a single command:
tshark -r capture.pcap \
    -o "http.tcp.port:8080" \
    -o "tls.port:8443" \
    -o "tcp.check_checksum:false" \
    -o "ip.check_checksum:false" \
    -o "tls.keylog_file:/tmp/keys.log" \
    -Y "http or tls"
Debugging Preference Issues:
# Check if preference was applied
tshark -o "http.tcp.port:8080" -G currentprefs | grep "http.tcp.port"

# Verify preference name is correct
tshark -G defaultprefs | grep -i "http.*port"

# Test with verbose output
tshark -o "nonexistent.preference:value" -v 2>&1 | grep -i preference
See Also:
- Reports (-G) for discovering available preferences
- TLS Decryption for TLS-specific preferences
- WPA2 Decryption for wireless preferences
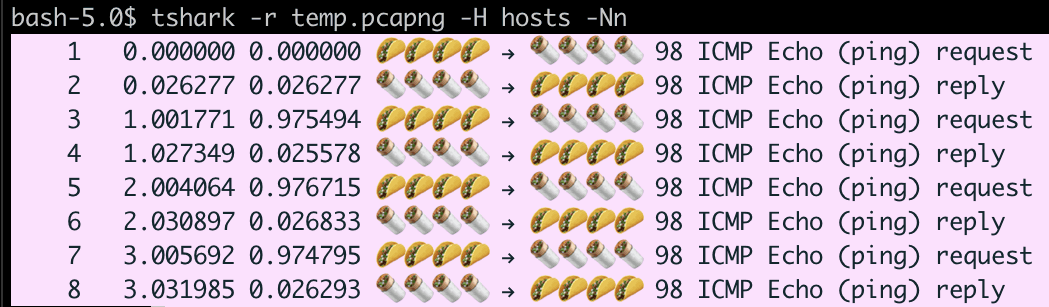
-H ${hosts}
Specify a hosts file by name. Let’s say that burritos and tacos found their way into our hosts file. I don’t know how, but it was delicious.
127.0.0.1       localhost
192.168.1.246   🌮🌮🌮🌮
8.8.8.8         🌯🌯🌯🌯
And we have a capture with 4 pings and responses to 8.8.8.8. Using -H and -Nn we can see these entries.
Further Reading
- 2014-07-01, Roy Cheok, Wireshark: A Guide to Color My Packets